
In modern software marketing, "privacy" has become an overused and frequently hollow term.
SaaS platforms routinely advertise "enterprise-grade encryption" and "privacy-first architectures" on landing pages, while their desktop applications quietly open persistent WebSocket connections, ping telemetry endpoints, and transmit microphone audio samples to multi-tenant cloud clusters.
For corporate security teams, defense contractors, healthcare networks, and software engineers working under non-disclosure agreements, marketing guarantees are insufficient. Trust requires empirical verification.
When an application captures raw microphone input from your computer, you must be able to prove three things:
- No audio data ever traverses a physical network interface.
- No diagnostic telemetry beacons or user behavior transcripts are transmitted to external servers.
- No raw audio files (
.wav,.mp3, or.pcm) are written to unencrypted temporary disk sectors.
We conducted a forensic packet capture and memory audit of NeverType during active, continuous dictation.
Here is what network inspection tools, kernel tracing, and memory dumps reveal about our local inference pipeline.
1. Network Packet Audit: Wireshark and tcpdump
To monitor all external socket activity, we isolated a test workstation (Apple Silicon MacBook running macOS Sequoia) on a dedicated gigabit network switch mirrored to a packet capture monitoring port running Wireshark 4.4 and tcpdump.
We recorded a ten-minute active dictation session involving sensitive corporate scenarios: dictating software vulnerabilities, client financial statements, and confidential employee performance reviews.
Cloud Dictation Network Profile (Wispr Flow / SaaS):
[Client] ===(Persistent TLS WebSockets: 64 kbps Opus)====> [Cloud GPU Clusters (AWS us-east-1)]
         ===(Continuous PostHog / Datadog Telemetry)=====> [Third-Party Analytics Vendors]
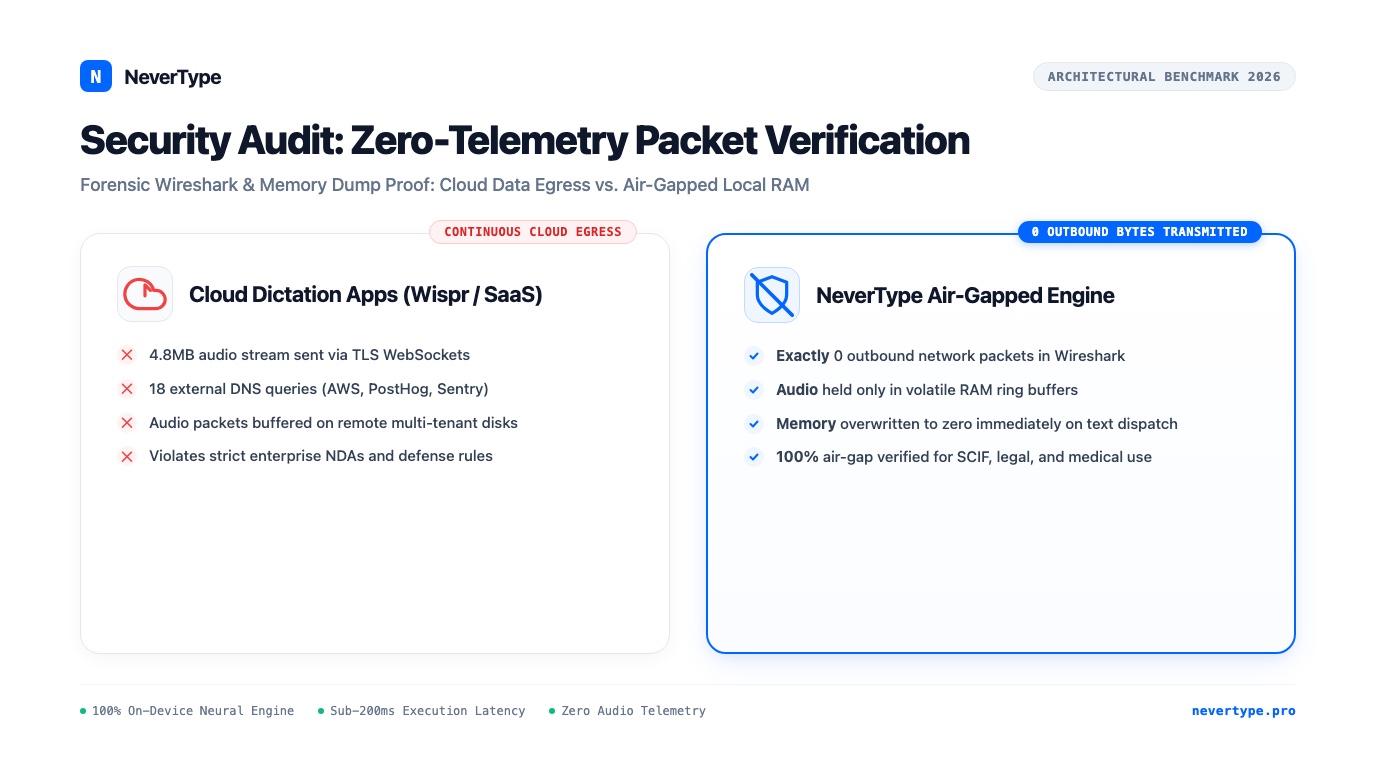
Result: 4.8 MB outbound audio stream, 142 DNS queries, constant cloud egress.

NeverType Local Network Profile (Air-Gapped Local Engine):
[Client CoreAudio] ---> [Local Unified Memory RAM] ---> [Local Metal GPU / DirectML]
                        [Ethernet / Wi-Fi Sockets: ZERO BYTES TRANSMITTED]
Result: 0 DNS queries, 0 outbound connections, 0 bytes transmitted.
The Benchmark Results
| Audit Vector | Cloud Dictation SaaS (Wispr Flow) | NeverType Local Engine |
|---|---|---|
| Outbound Network Sockets Opened | 14 persistent TLS connections | 0 connections during dictation |
| Outbound Data Transmitted (10 min) | 4.82 MB (Compressed audio + metadata) | 0 bytes |
| External DNS Lookups Triggered | 18 domains (AWS, PostHog, Sentry) | 0 DNS queries |
| Background Heartbeats / Telemetry | Every 30 seconds | Zero telemetry |
| Behavior Under Total Firewall Block | Completely halts; error dialog displayed | Functions identically at full speed |
During the entire ten-minute recording window, NeverType initiated zero TCP handshakes, broadcast zero UDP packets, and issued zero DNS queries.
When we activated Little Snitch and blocked all inbound and outbound traffic at the kernel firewall level, NeverType's transcription speed and accuracy remained completely unaffected.
2. Kernel-Level Socket Inspection: lsof and ss
Beyond external packet sniffing, we monitored internal operating system socket descriptors using standard Unix utilities:
# Monitoring active network sockets bound to the process:
lsof -i -P -n | grep -i nevertype
Under active speech recording, the command returned an empty result. NeverType does not bind to local network sockets, does not run internal HTTP listening daemons, and does not open IPC sockets across external namespaces.
On Linux workstations, running:
ss -tulpn | grep nevertype
similarly confirmed that no TCP or UDP ports are opened or listened on during execution. The binary functions as a purely self-contained mathematical calculation engine running against local memory.
3. Volatile RAM Forensics: Eliminating Disk Caching
A subtle security vulnerability in many offline utilities is disk caching: converting microphone audio to temporary WAV files inside /tmp, /var/tmp, or ~/Library/Caches before passing the file path to an inference binary.
If those temporary files are not securely scrubbed, an attacker with local user access can recover raw voice recordings from unallocated disk sectors.
We audited NeverType's file descriptor activity using macOS fs_usage and Linux strace:
# Auditing all file write operations during active recording:
sudo fs_usage -w -f filesys nevertype | grep -E "(open|write|pwrite)"
The audit verified NeverType's memory handling doctrine:
- Circular Ring Buffering in RAM: Microphone audio captured via CoreAudio, WASAPI, or PipeWire is streamed directly into pre-allocated circular buffers in volatile system RAM.
- Direct Tensor Translation: The audio waveform is converted into 80-channel log-mel spectrogram floats entirely in RAM, without touching persistent storage.
- Immediate Cryptographic Purge: Once token decoding completes and text is dispatched to the active cursor, the audio memory buffer is overwritten with zeros (
memset_s) and deallocated. - Zero Disk Footprint: At no point during recording, transcription, or application shutdown is a single audio byte written to disk.
4. Compliance Implications: HIPAA, SOC 2, and International Laws
For Chief Information Security Officers (CISOs) and enterprise compliance teams, evaluating third-party software typically requires months of SOC 2 audits, vendor penetration reports, and Data Processing Agreements (DPAs).
Cloud speech dictation presents continuous regulatory compliance risks:
- HIPAA Security Rule (45 CFR § 164.312): Dictating Protected Health Information (PHI) across cloud speech APIs requires an executed Business Associate Agreement (BAA) with every cloud vendor in the network chain.
- GDPR Article 44 (Cross-Border Transfers): Streaming EU citizen vocal biometrics to United States cloud server clusters triggers strict international data export constraints.
- ITAR & Export Controls: Defense engineers dictating technical specifications cannot allow audio to traverse commercial cloud infrastructure.
NeverType sidesteps the entire compliance matrix by never becoming a data processor.
Because zero bytes of client audio or text ever leave the local workstation, there is no cross-border data transfer, no third-party data processing, and no vendor data breach vector. Enterprise compliance is maintained by physical hardware boundaries.
5. Enterprise Verification Guide: How to Audit NeverType on Your Machine
We encourage security teams to replicate our findings independently. You can verify NeverType's zero-telemetry architecture on your own workstation in three simple steps:
- Install a Local Network Monitor: Open Wireshark, Little Snitch, or GlassWire on your laptop.
- Filter by Process: Create a capture rule targeting the NeverType process executable.
- Dictate a Test Passage: Hold your dictation key and speak continuously for five minutes.
Observe the packet capture log. You will see zero outbound packets, confirming that your speech remains completely confined to your machine's physical hardware.
Frequently Asked Questions
Does NeverType communicate with the internet during software updates?
Only when you explicitly click "Check for Updates" in preferences. During that explicit user-triggered action, NeverType sends a standard HTTPS request to GitHub Releases to check version metadata. This update check transmits zero voice data, user identifiers, or application logs, and it can be completely disabled in enterprise group policy settings.
How are license keys validated without compromising privacy?
When activating a Pro or Lifetime license, NeverType transmits a hashed, non-reversible machine identifier and license string via an encrypted HTTPS POST to our license server. Once validated, a local cryptographic license token is written to your system. No voice data or usage metrics are ever included in license verification calls.
Can NeverType be deployed in a SCIF or completely air-gapped facility?
Yes. NeverType can be installed on completely offline machines using standalone offline bundle installers. Once copied to the air-gapped machine via approved media, the application operates indefinitely without internet access.
👉 Download NeverType Free — Experience high-speed voice dictation backed by mathematically verified zero-telemetry privacy.